– A white paper from CEO to CEO
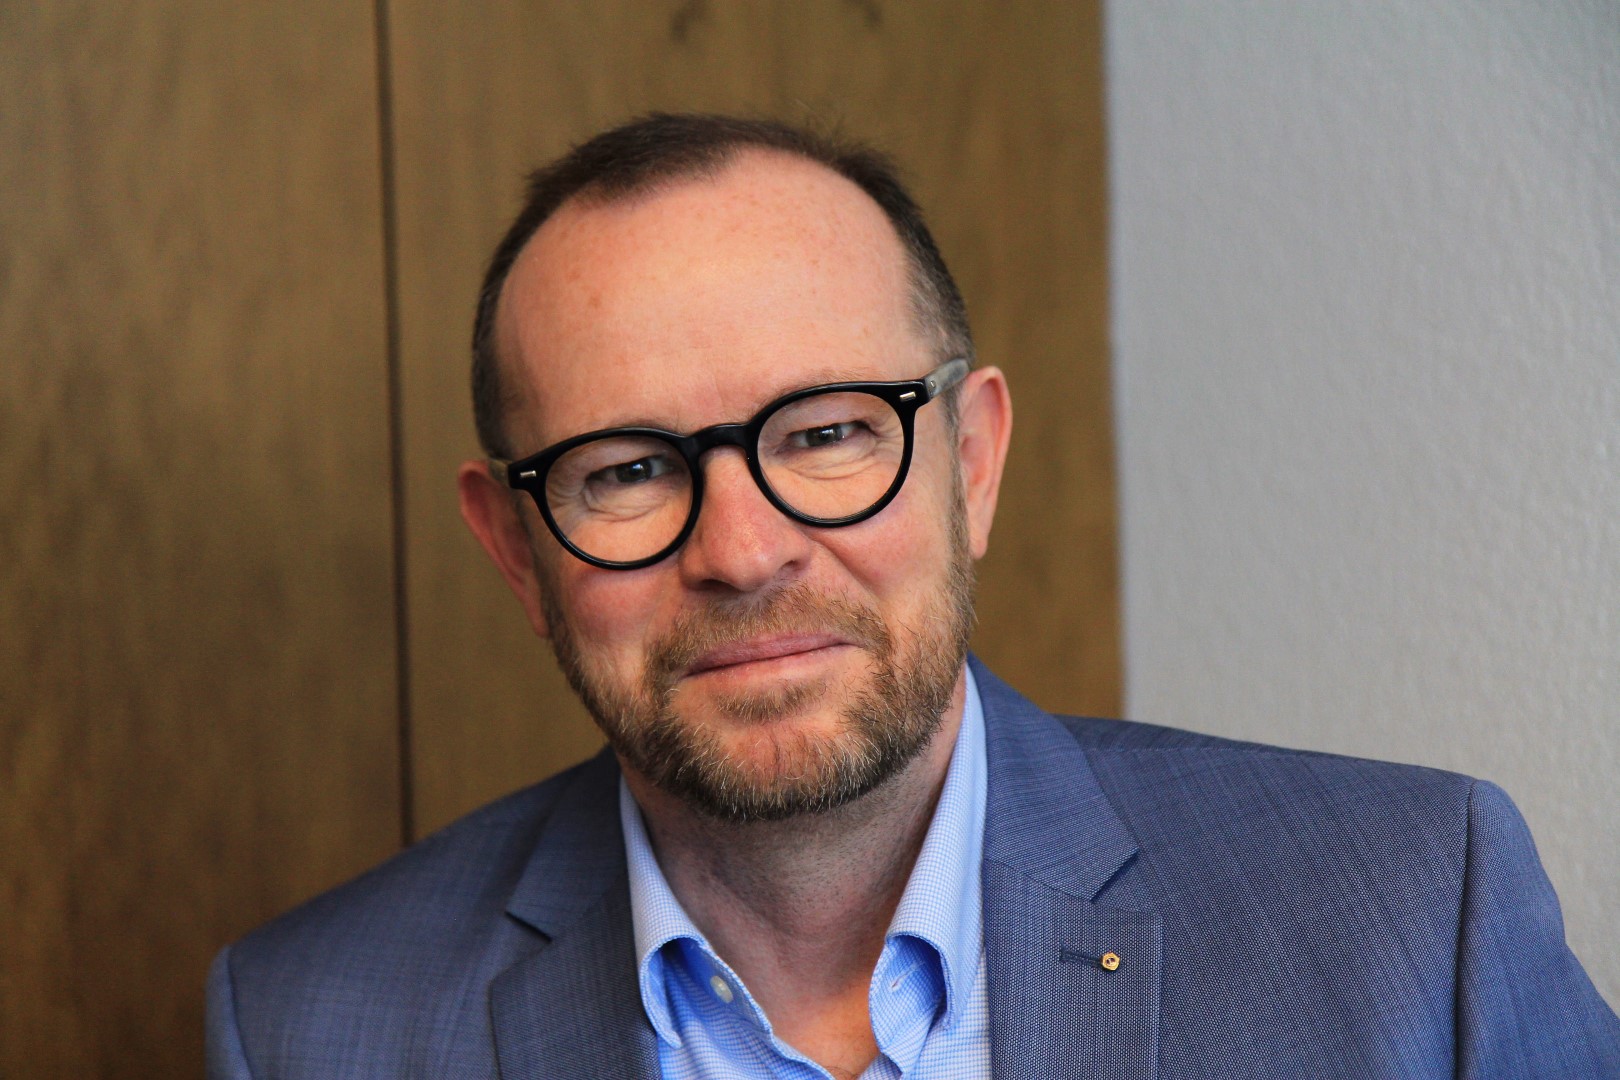
Thomas Weihrich, CEO, Weihrich Informatik
September 17, 2026
Foreword: A Letter from One CEO to Another
This text was automatically translated
As the founder and CEO of Weihrich Informatik, I have been talking for years with decision-makers at SMEs about an issue that is becoming increasingly urgent: IT security. From family-owned businesses with 50 employees to international service providers with 1,000, I hear the same statement: “We know we need to take action—but we don’t know where to start.” That is precisely what this white paper is about: seven proven areas of focus for IT security in SMEs.
Here is my answer. I’m not writing this as a salesperson, but as a colleague who understands the concerns of a business owner from my own experience: responsibility for employees and customers, limited resources, and the need to position the company for a secure and sustainable future. What I’m about to describe are seven areas of action that I consider the most important today. None of them is a vision—all are proven, affordable, and feasible in companies like yours.
1. The Current Situation:
Attacks that are faster than any manual response
Let’s be honest: The threat landscape has changed fundamentally in recent years. Attackers are using artificial intelligence to automatically find and exploit vulnerabilities. Phishing messages are now so well written that even trained employees can barely tell them apart from genuine business emails. The time between the start of an attack and its potential success has shortened dramatically. When just a few minutes determine whether sensitive company data is compromised, purely manual monitoring is no longer sufficient.
On top of that, there are three trends I’ve observed in nearly every company: Employees work from anywhere, and their devices constantly switch between the corporate network and third-party Wi-Fi networks. Many use AI tools via personal accounts without the IT department’s knowledge. And many Microsoft 365 environments are running with default settings that are no longer sufficient to withstand this level of threat.
That’s why IT security is now a top priority for executives. Not because you have to configure firewalls yourself—but because only senior management can make the necessary decisions, set priorities, and approve budgets. And it’s more than just a formality: Those who professionally protect their IT environment position themselves as reliable partners in the marketplace. Customers, suppliers, and partners rightly expect their data to be in safe hands.
2. Action Area 1:
Clarity Instead of Assumptions—The Safety Analysis
Security starts with knowing where you stand today. In many companies, the sense of security is based on assumptions: “Our provider takes care of it,” “We’re too small to be a target for attackers,” “The backup is working, after all.” Assumptions are not a sound basis for decisions that affect your company.
A thorough analysis scan examines your entire IT architecture for hidden vulnerabilities, outdated protocols, and potential entry points. The result is not an obscure list of error logs, but a clear analysis that tells you, in management terms: These areas are well-positioned; here, there is an urgent need for action.
Building on this, we create a security package tailored precisely to your business—with proactive monitoring, state-of-the-art firewall solutions, and multi-factor authentication. The big picture is crucial here: IT must not be a patchwork. When systems do not integrate seamlessly, it not only leads to inefficiencies in day-to-day operations but, more importantly, creates dangerous security vulnerabilities that attackers can exploit.
3. Action Area 2:
Consistently Strengthen Microsoft 365
Many Microsoft 365 environments are set up correctly from a functional standpoint but have significant gaps in their security configuration. The reason is simple: New security features from Microsoft are generally not enabled automatically. What was considered secure a year ago may now be a preventable security vulnerability.
The Microsoft Secure Score transparently shows how well your tenant is protected. We don’t view this score as a static number, but rather as an ongoing mission: to disable unused features, strictly regulate access rights, and enforce security standards across the board. Specifically, this means: limiting administrative privileges to the absolute minimum, disabling outdated authentication protocols, consistently configuring threat defense and data encryption, and continuously monitoring login activity.
My advice: Have your Microsoft 365 environment checked regularly by experts. The investment is negligible compared to the damage caused by a compromised tenant.
4. Action Area 3:
Protecting Identities – Strong Multi-Factor Authentication
Protecting access rights is no longer an option; it is the foundation of every security strategy. Stolen or guessed login credentials are among the most common points of entry.
Cisco Duo Essentials provides the foundation: phishing-resistant multi-factor authentication and device verification before every login. Thanks to over 500 pre-built application integrations, Duo Essentials can be quickly deployed in virtually any environment—without months-long projects.
Duo Advantage goes significantly further. At its core is Cisco Identity Intelligence (CII): It consolidates identity data from the on-premises Active Directory and cloud sources such as Entra ID, Okta, or Google Workspace into a comprehensive view of your identity landscape. Specifically, this means the system also protects legacy protocols that do not support modern MFA. It detects forgotten or overprivileged administrator accounts that would otherwise go unnoticed and become persistent attack vectors. It detects suspicious login patterns and lateral movement by attackers within the network—thanks to AI-powered ITDR (Identity Threat Detection and Response). And it identifies gaps between local AD and cloud identities (Identity Security Posture Management).
In short: Essentials secures the login, while Advantage secures the entire identity.
5. Action Area 4:
Automated Response – SOC, SOAR, and Endpoint Protection
If your system detects a specific threat, it cannot wait for a technician to intervene—especially if that technician is off on the weekend or on vacation.
A SOC (Security Operations Center) is the central security control center where all data streams converge. There, unusual activity is immediately detected, assessed, and classified. SOAR (Security Orchestration, Automation, and Response) connects your individual security systems and automates response workflows: If the SOC detects an imminent threat, the appropriate countermeasure is implemented without delay.
The same principle applies to end devices: If a device exhibits suspicious behavior or reports an infection, it is automatically disconnected from the company network. The damage remains confined to that device; the rest of the infrastructure remains intact, and your employees can continue working.
For you as management, this means: You’re not just buying technology, but time—the most valuable resource in any security incident.
6. Action Area 5:
Staying Safe on the Road – Protecting Mobile Work Equipment
As soon as a laptop, tablet, or smartphone leaves the company network, central firewalls and DNS filtering often no longer apply. When connected to Wi-Fi at a hotel, in a coworking space, or at a client’s location, these devices are left to fend for themselves. The risk of phishing and malware increases significantly.
The answer is SecureEdge, a cloud-first SASE platform that moves security capabilities directly to the cloud. Regardless of location, every device benefits from the same high standard of protection as at a fixed workstation—without any loss of performance or obstacles to daily work. Your employees won’t even notice the protection—except that they can work securely.
This is the most advanced way to extend the protection of central IT to the mobile world, especially for companies with 50 to 1,000 employees that operate in a hybrid model or across multiple locations.
7. Action Area 6:
Shadow AI – Transparency Instead of Uncontrolled Data Leakage
Many of your employees use ChatGPT, Claude, or Perplexity—often through personal accounts, outside the control of the IT department. This is rarely done with malicious intent: When employees don’t have access to approved AI tools, they find their own ways. The tools are useful, and their intentions are usually sincere.
The result is nonetheless an uncontrolled outflow of data: Public AI models are trained using the information entered. Internal documents, customer data, or trade secrets thus leave the company’s secure environment—irreversibly.
A strict ban is rarely the solution. It creates underground channels instead of protecting data. The better approach: foster transparency, assess actual usage, and steer AI use in a safe direction—with clear guidelines, employee awareness training, and secure, approved alternatives. This way, your team benefits from the increased efficiency provided by AI, while your data remains protected.
8. Action Area 7:
Ready to Act in an Emergency—The Disaster Recovery Plan
A power outage, a cyberattack, or a serious hardware failure can bring your business to a sudden halt. The question isn’t whether an emergency will occur, but whether you’ll be able to respond effectively when it does.
The Disaster Recovery Plan (DRP) outlines what happens in the event of an emergency: clearly defined responsibilities, reliable communication channels, and strictly prioritized procedures. It answers the questions that leave no time for discussion during a crisis: Who makes the decisions? Who notifies employees, customers, and authorities? Which systems must be restored first?
The development of a DRP begins with a candid assessment: risk analysis, evaluation of the most critical business processes, and definition of maximum downtime and tolerable data loss. This leads to technical solutions—such as redundant systems and off-site backups—as well as organizational guidelines.
And a plan is only as good as its implementation: Regular testing is essential, because a contingency plan from three years ago no longer covers today’s risks. The DRP is a living document that grows with your company.
9. An Overview of the Seven Areas of Action
| Area of Action | Key Question | Centralized Solution |
| Security Analysis | Where do we stand today? | Vulnerability Scan and Customized Security Package |
| Microsoft 365 | Is our tenant really hardened? | Secure Score as an Ongoing Task |
| Identities | Who actually gets in? | Cisco Duo Essentials and Advantage with Identity Intelligence |
| Automated Response | What happens in an emergency? | SOC and SOAR with Automatic Decoupling |
| Mobile Devices | Are we protected even when we’re outside? | SecureEdge as a Cloud-First SASE Platform |
| Shadow AI | Where does our data go? | Transparency, Guidelines, Safe Alternatives |
| Emergency Plan | Are we capable of taking action? | Disaster Recovery Plan with Regular Tests |
10. Conclusion: Your Next Step
IT security is not a project with an end date, but rather an ongoing process. The seven areas of action cover the entire spectrum: from conducting an assessment to protecting identities, platforms, and mobile devices, to automated defense and the ability to respond in an emergency.
In my conversations with business owners, one thing stands out: Many of their competitors neglect their systems. This presents an opportunity. Those who professionally strengthen their operations position themselves as a reliable player within the industry—in the eyes of customers, partners, and in competitive bids.
My recommendation as a colleague: Start by taking stock of the situation. It provides clarity, costs very little, and shows you the way forward. You don’t have to tackle everything at once—but you should know where you stand.
At Weihrich Informatik, we speak your language, explain complex issues in a way that’s easy to understand, and take real responsibility—from initial planning through integration to support. Talk to your IT team; give me a call or send me an email: Let’s discuss 7 areas of focus that will help you and your business move forward! For more information, visit the “News – Weihrich Informatik ” section at https://www.weihrich.ch/loesungen/it-komplettloesungen/
Yours,
Thomas Weihrich, CEO, Weihrich Informatik
Contact:
Thomas Weihrich
Alleestrasse 20
CH 8280 Kreuzlingen
t.weihrich@weihrich.ch
T +41 71 688 33 30
M +41 79 313 13 63